Information Security Risk Management in Practice: Building a Register Your Team Will Actually Use
Plenty of small companies know they should manage risk and still never do it, because the advice they find is written for enterprises with compliance departments. The numbers reflect that gap: a 2025 Techaisle SMB report found 51% of small and medium businesses lack a formal risk framework, and 28% have little to no discussion about risk management at all. The practical version is far smaller and more useful. information security risk management, as CodeRed’s intermediate course frames it, comes down to a repeatable cycle you can run on a single living document, and this article is about building that document so your team actually keeps it open.
The goal here is not theory. It is a risk register that a real small team maintains without a dedicated analyst, survives busy weeks, and genuinely changes decisions. Most registers fail not because the idea is wrong but because they are built to impress an auditor instead of to be used, and that is the mistake this walkthrough avoids.
What Is a Risk Register, Really?
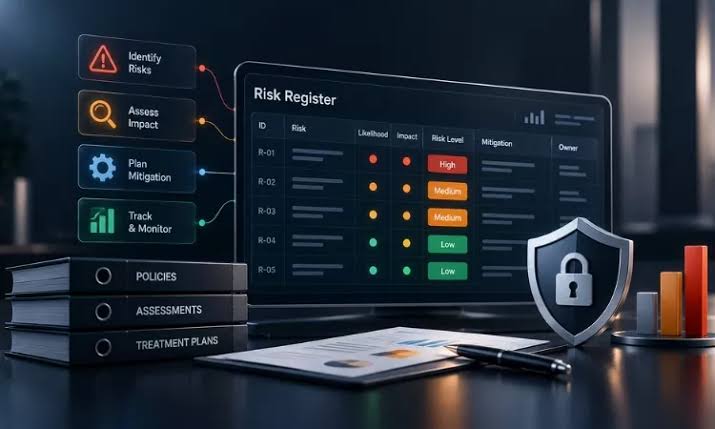
A risk register is simply a list of what could go wrong, how bad it would be, and what you are doing about each item. Strip away the enterprise formatting and it is a prioritized to do list for things that threaten your data and operations.
The CodeRed risk management course describes the underlying cycle directly: identifying, assessing, treating, and monitoring risks. A register is just where that cycle lives on paper. Everything else is detail, and for a small business most of that detail is optional.
Where Do the Entries Come From?
They come from knowing what you are protecting first. This is where foundational thinking pays off, and CodeRed’s beginner business cybersecurity course is useful groundwork, because it frames protection around identifying critical data and the realities a small company faces.
Start with your most important systems and data, then for each one ask what could realistically harm it. A leaked customer database, a frozen invoicing system, a compromised email account: each becomes an entry. You are not trying to list every conceivable threat, only the ones that would actually hurt this business.
How Do You Keep It Simple Enough to Survive?
The trick is deliberate minimalism. A register with twelve clear entries that people read beats one with two hundred that nobody opens. Each entry needs only a few fields to be useful:
- The risk, in one plain sentence.
- How likely and how severe, rated simply as low, medium, or high.
- The treatment, meaning what you are doing: reducing, transferring, accepting, or stopping the activity.
- The owner, one named person accountable for it.
That is enough. Anything heavier tends to get abandoned the first time the team is busy, which is precisely when the register matters most.
Who Owns It, and How Often Is It Touched?
One person owns the register overall, and each entry has its own owner, even in a small team. Shared ownership with no name attached is how risks quietly become nobody’s job. The overall owner keeps the document honest; the entry owners handle their specific items.
Touch it on a schedule, not on willpower. A thirty minute review each quarter, plus a quick update whenever something changes, like a new vendor or a new system, keeps it alive. The review is short on purpose, because a long one gets postponed and a postponed review becomes a dead document.
What Makes a Register Actually Get Used?
It gets used when it changes real decisions. If the register sits in a folder and never informs a choice, it is theater. The fix is to bring it into the moments where decisions already happen: before signing a new vendor, before launching a system, during budget planning.
When someone proposes a new tool, the register is where you note what data it touches and what could go wrong. When money is tight, it is how you decide which protection to fund first. A document that feeds those conversations earns its place. One that does not will always lose to more urgent work, no matter how well formatted it is.
Making It a Habit Rather Than a Project
The difference between a register that works and one that dies is whether it becomes routine. Treat it as a short, recurring rhythm rather than a one time project with a finish line, and it quietly compounds in value as the business grows around it.
Made-up example: a fifteen person agency builds a twelve entry register in an afternoon, assigns an owner to each line, and reviews it for half an hour every quarter. A year later, when a client asks how they manage security, they have a clear, honest answer ready. A similar firm that built an elaborate forty page register abandoned it within two months and had nothing to show when the same question came. The smaller, living document won, precisely because it was small enough to keep alive.

Post Comment